Cybersecurity built in Europe, ready for your next audit

For DSI and RSSI teams facing EU regulatory compliance requirements, who need audit-ready proof and far less day-to-day maintenance.
THE CHALLENGE

Secure hybrid IT and meet audit and regulatory requirements

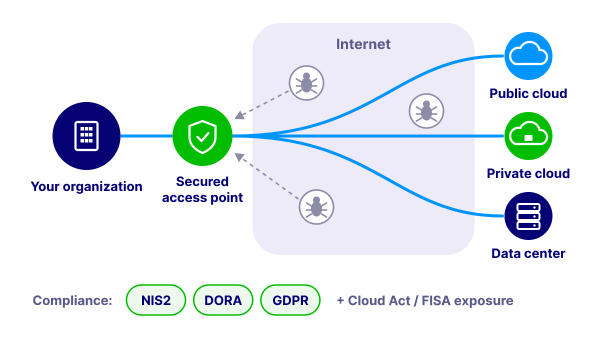
Cyberattacks are growing more advanced and more destructive, and organizations of all sizes must strengthen their defenses. As businesses rely on Internet access to reach critical applications hosted across public clouds, private clouds and data centers, securing these access points has become essential.

The expansion of hybrid cloud infrastructures has multiplied the attack surface and strained network performance, putting application QoS and QoE at risk. Any outage, misuse or breach can immediately impact revenue, brand reputation and operational continuity.

Traditional web security still catches threats only once they’ve been identified, while over 400,000 new malware variants and 13 million malicious domains appear every month, faster than any signature-based filter can keep up. European regulation has also raised the burden of proof for essential and important entities under NIS2, financial institutions under DORA and any organization handling personal data under GDPR, while non-European cloud vendors remain exposed to extraterritorial laws like the US Cloud Act and FISA.

USE CASES

Where this makes the biggest difference

Ekinops SASE delivers streamlined network performance optimization along with advanced security capabilities including the best protection against web traffic risks – ideal for organizations looking to reinforce their security without the burden of complex operations.

Benefits

What Ekinops Trusted European Cybersecurity delivers

FAQ

Find your answer to common questions on our cyber solution.

Ekinops centralizes full traceability of application access and web traffic through timestamped, encrypted, user-level event logs. The SSE automatically inventories Shadow IT and Shadow AI usage while ZTNA enforces least-privilege access and generates audit-ready compliance reports. Because all data and logs are hosted in Europe, this traceability meets NIS2’s logging requirements and DORA’s third-party risk management obligations without extra work.

Traditional UTMs treat web filtering as a secondary feature that competes for the appliance’s processing power, and traditional VPNs grant broad access to an entire subnet once a user connects. Ekinops’s approach breaks from both. Zero Trust Internet Access blocks everything by default and only allows traffic to verified, known-good domains, drawing on a database of over a billion classified URLs, rather than trying to catch every new threat by signature. Zero Trust Network Access exposes no port or server to the internet at all, cutting the attack surface by around 80% and removing the risk of lateral movement.

On a legacy VPN and multi-site UTM setup, IT teams spend real time rewriting firewall rules, managing IPsec tunnels, and keeping heavy client agents updated. Ekinops’s Universal ZTNA replaces that with a cloud-native, identity-driven architecture: agents deploy remotely at scale, updates happen transparently in the cloud, and SaaS application discovery is automated. According to Ekinops product testing, that cuts the time needed to maintain and operate remote access by around 5 times compared with legacy VPN and UTM setups.
Yes. Ekinops SASE is designed to support Managed Service Providers (MSPs) and Global System Integrators (GSIs) delivering security services to multiple customers. Through its multi-tenant native architecture, service providers can centrally manage, monitor, and operate separate customer environments while maintaining tenant isolation and delegated administration. This enables the delivery of managed security services, including SOC-related monitoring, incident response workflows, policy management, and reporting.

LET'S TALK

Ready for cybersecurity that's audit-ready and actually easy to run?